@DelCrxpto ↔ @FabioS15 ↔ @Vlad52673095 conversation

DelCrxpto@DelCrxpto
8 views
Nov 11, 2026
~2 min read
Advertisement
DelCrxpto@DelCrxpto
Today irrefutable evidence was discovered that @Ledger is not a cold wallet.
Evidence indicates that @Ledger devices send signals to @Ledger allowing @Ledger to store information that can compromise the safety and security of your private keys.
I have been saying this for years, but now it has been proven.
Evidence indicates that @Ledger devices send signals to @Ledger allowing @Ledger to store information that can compromise the safety and security of your private keys.
I have been saying this for years, but now it has been proven.

FabioS@FabioS15
What hardware do you recommend?
Or what multi Sig?
Or what multi Sig?
DelCrxpto@DelCrxpto
The thesis that I learned taught me that crypto cold storage is optimized when you keep your crypto behind keys that have no authorizations or signatures.
I learned the thesis here:
storage.koini.io
I am able to check every Wallet address I have for authorizations and signatures, free, here: keystate.koini.io
I learned the thesis here:
storage.koini.io
I am able to check every Wallet address I have for authorizations and signatures, free, here: keystate.koini.io

Vlad@Vlad52673095
using multi-sig wallets is a great idea. xaman has multisig for XRP. vultisig wallet has multi-sig for multiple cryptos. lobstr+vault is great multisig wallet for stellar chain / xlm.
don't rely on one seedphrase to protect your crypto. the days of hardware wallets is over.
don't rely on one seedphrase to protect your crypto. the days of hardware wallets is over.
DelCrxpto@DelCrxpto
Personally, I disagree.
The thesis I learned for optimized crypto cold storage teaches that crypto cold storage is optimized when your crypto sits behind keys that have absolutely no authorizations and no signatures.
Multisig is literally the exact opposite of that and has been hacked more times than can be counted.
Learn more here: storage.koini.io
The thesis I learned for optimized crypto cold storage teaches that crypto cold storage is optimized when your crypto sits behind keys that have absolutely no authorizations and no signatures.
Multisig is literally the exact opposite of that and has been hacked more times than can be counted.
Learn more here: storage.koini.io
Vlad@Vlad52673095
do you have any proof of "consumer" wallet multisig hacks? i've been researching and so far can't find any. can you share any examples?
regarding cold storage, most people improperly use hardware wallets for daily transfers, walletconnect, defi, contracts/approvals...
regarding cold storage, most people improperly use hardware wallets for daily transfers, walletconnect, defi, contracts/approvals...
DelCrxpto@DelCrxpto
absolutely...
years & years worth of evidence has been well documented in the space.
I even know consumer multi-sig wallets there were hacked recently as weeks ago.
however, there has NEVER been a wallet hacked that had no authorizations or signatures, ever in the history of blockchain.
years & years worth of evidence has been well documented in the space.
I even know consumer multi-sig wallets there were hacked recently as weeks ago.
however, there has NEVER been a wallet hacked that had no authorizations or signatures, ever in the history of blockchain.
Vlad@Vlad52673095
again, can you give me examples of consumer multi-sig wallets that were hacked?
attached Grok response. for institutions it's true. but for consumer no successful public hacks resulting in drained user funds have surfaced
@vultisig are you aware of any recent multisig breaches?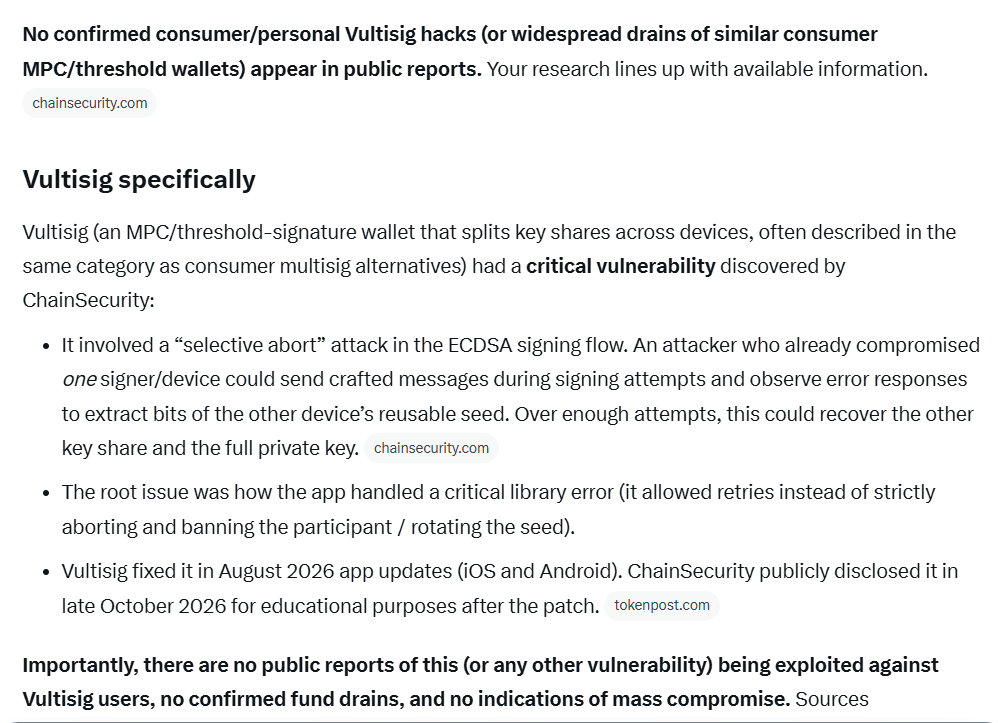
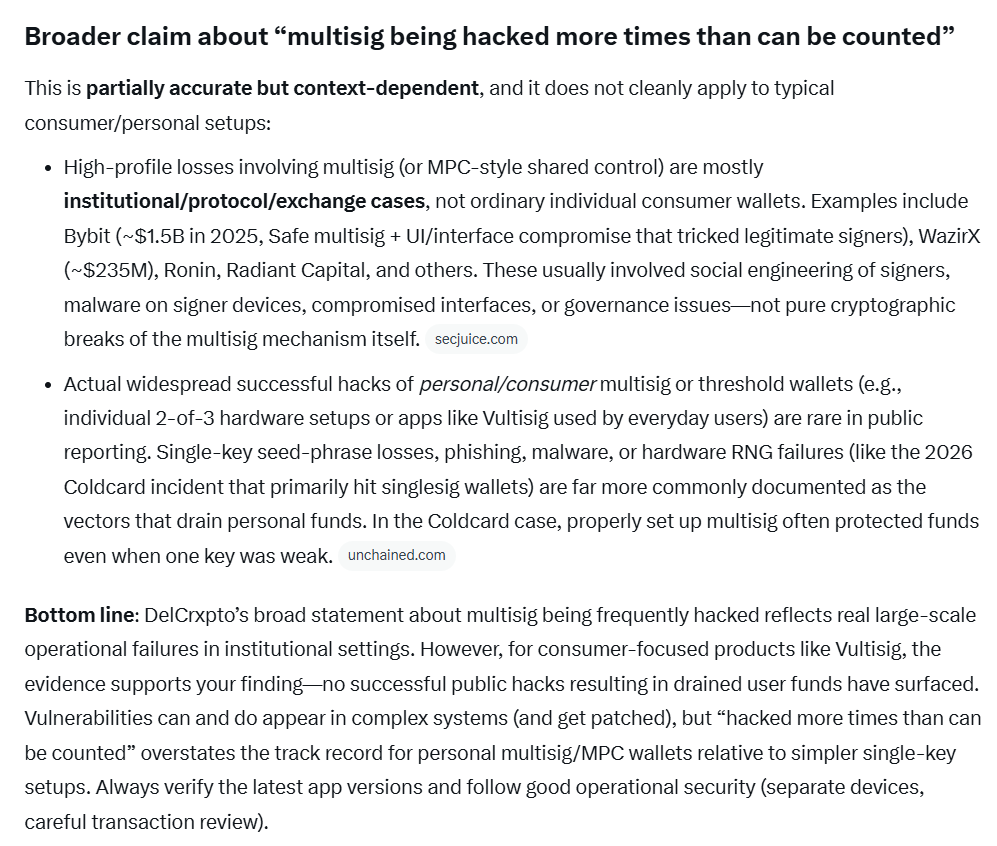
attached Grok response. for institutions it's true. but for consumer no successful public hacks resulting in drained user funds have surfaced
@vultisig are you aware of any recent multisig breaches?


