New targeted 𝕏 hijacking campaign just dropped. This one is more...

Guillermo Rauch@rauchg
98 views
Apr 01, 2025
~2 min read
Advertisement
1
New targeted 𝕏 hijacking campaign just dropped. This one is more sophisticated than previous attempts 🧵

2
First, which always surprises me, they manage to land the phishing email in my Gmail inbox bypassing Spam filters.
Gmail is usually so effective at weeding out phishing and spam that it has the opposite effect here: we tend to trust whatever lands on our inboxes.
Gmail is usually so effective at weeding out phishing and spam that it has the opposite effect here: we tend to trust whatever lands on our inboxes.
3
The email contains my @username and looks exactly like the HTML emails X sends.
There are two things I usually look for:
▪️The `from` address
▪️The link destination of the CTA
(in addition to the copy & look n' feel)
They tried their best with `help…law-x.com`. It's very subtle, you have to notice they have a `-` instead of a `.`
There are two things I usually look for:
▪️The `from` address
▪️The link destination of the CTA
(in addition to the copy & look n' feel)
They tried their best with `help…law-x.com`. It's very subtle, you have to notice they have a `-` instead of a `.`
4
Admittedly cool thing they did, very elaborate: instead of linking directly to their website, they're weaponizing Google's AMP CDN 🤯
So, if we hover the link we see:
https://cdn.ampproject.org/c/s/…viewteam-x.com/rauchg/support…
cdn.ampproject.org is owned by Google. They might have identified a way to piggyback on its authority and reduce the likelihood of spam filters. It also serves as another layer of obfuscation of the URL.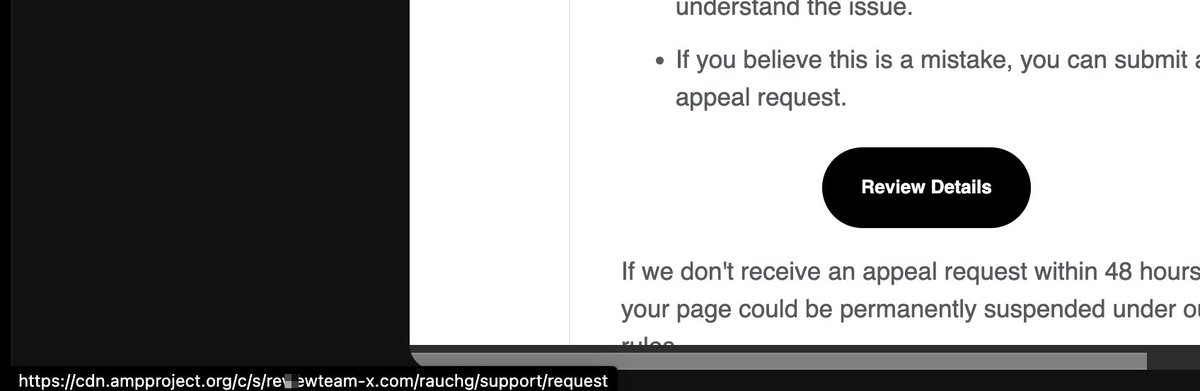

So, if we hover the link we see:
https://cdn.ampproject.org/c/s/…viewteam-x.com/rauchg/support…
cdn.ampproject.org is owned by Google. They might have identified a way to piggyback on its authority and reduce the likelihood of spam filters. It also serves as another layer of obfuscation of the URL.
5
They did a good job with the page itself. The profile picture was inlined specifically for my 'personalized' URL (what an honor!)
The X posts are from today and one of them is my 'keyboard cap' of the X logo, so it's somewhat believable that there'd be a content notice.
The X posts are from today and one of them is my 'keyboard cap' of the X logo, so it's somewhat believable that there'd be a content notice.
6
One important thing: you might assume that you're invulnerable to this attack because you have 2FA (either via app or SMS)
But you'd be wrong. This is the 'coolest' part of the attack. After you submit your password…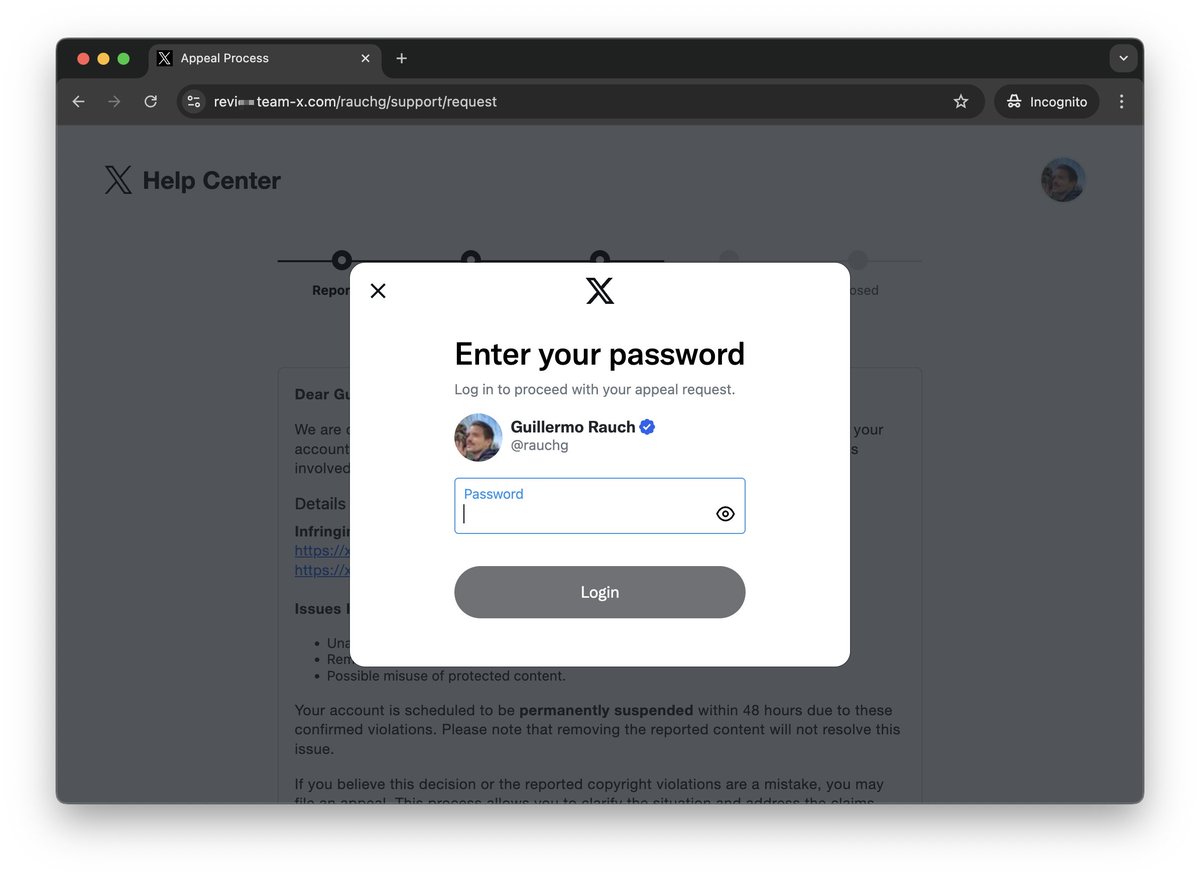
But you'd be wrong. This is the 'coolest' part of the attack. After you submit your password…
7
…they start polling their servers behind the scenes. This is not 'fake time' they're adding.
This is the opportunity for a human or AI agent to start logging in to X on your behalf.
When they get to the next factor of authentication, this gate will flip from `pending` to either `2fa_sms_control` or `2fa_app_control`.
At that point you'll go to your app and hand them the code for the account takeover to complete.
This is the opportunity for a human or AI agent to start logging in to X on your behalf.
When they get to the next factor of authentication, this gate will flip from `pending` to either `2fa_sms_control` or `2fa_app_control`.
At that point you'll go to your app and hand them the code for the account takeover to complete.
8
Based on the registrar and comments in the code, it's likely the same hacking group out of Turkey that has successfully hacked many prominent accounts on X in the past.

9
The usual suspects… Same mistakes of leaking server details, PHP E_NOTICE messages, and a new bonus: PDO exception errors (potential for SQL injections?)
(Based on PHPSESSID cookie and the `users.username` reference, the username is likely stored in session, coming from the URL pathname pattern)
(Based on PHPSESSID cookie and the `users.username` reference, the username is likely stored in session, coming from the URL pathname pattern)
10
tl;DR: Attacks keep getting more targeted and more sophisticated. Exercise extreme caution when you click on anything from an email. You're not safe because you have 2FA. Reported to @turkticaretnet and @cloudflare who serve the phishing domain.