Last year, a friend was planning a trip to an amusement park for...

Rithwik Jayasimha@thel3l
45 views
Jan 18, 2025
~4 min read
Advertisement
1
Last year, a friend was planning a trip to an amusement park for her bday. Site design is often a good heuristic for security and the design wasn't inspiring confidence—so I went poking.
A fun story of finding a payment bypass in PayU India and the subsequent disclosure arc:

A fun story of finding a payment bypass in PayU India and the subsequent disclosure arc:
Rithwik Jayasimha@thel3l
In the coming day or two, I'll be sharing the full details on how it was possible to bypass PayU India's hosted checkout flow and get free stuff from any merchant
bonus: failed managed disclosure programs, my credit card being abused, and @IndianCERT being awesome!
bonus: failed managed disclosure programs, my credit card being abused, and @IndianCERT being awesome!
2
Some background: @PayUindia is one of the largest payment gateways, used by over 500k+ merchants online in India.
When you pay for things online, merchants will rely on PayU to say "Yes, we got da money!"—and trust that yes, they really did.
This becomes important later.
When you pay for things online, merchants will rely on PayU to say "Yes, we got da money!"—and trust that yes, they really did.
This becomes important later.
3
Now, the 'Transaction was successful' logic is often either handled with a webhook or a callback URL.
A good rule is to obviously never trust the client for any of this—the user is always going to try to scam you.
A good rule is to obviously never trust the client for any of this—the user is always going to try to scam you.
4
Back to the checkout:
I lazily played with payment values being sent to the gateway but realized that the parameters were all hashed with a salt: you could not just tweak the values and pass the transaction.
Now, see the 'furl' and 'surl' fields?
I lazily played with payment values being sent to the gateway but realized that the parameters were all hashed with a salt: you could not just tweak the values and pass the transaction.
Now, see the 'furl' and 'surl' fields?
5
So the client controls the success and failure callback URLs. But how is the hash computed?
The PayU docs at the time defined it as:
sha512(key|txnid|amount|productinfo|firstname|email|udf1|udf2|udf3|udf4|udf5||||||SALT)
Conspicuously absent: furl, surl in the hash.
The PayU docs at the time defined it as:
sha512(key|txnid|amount|productinfo|firstname|email|udf1|udf2|udf3|udf4|udf5||||||SALT)
Conspicuously absent: furl, surl in the hash.
6
Since the attcker controls the success and failure callback URLs, they could just swap their values, and a failed payment would trigger a successful action flow ...
There's no way that this would work, right?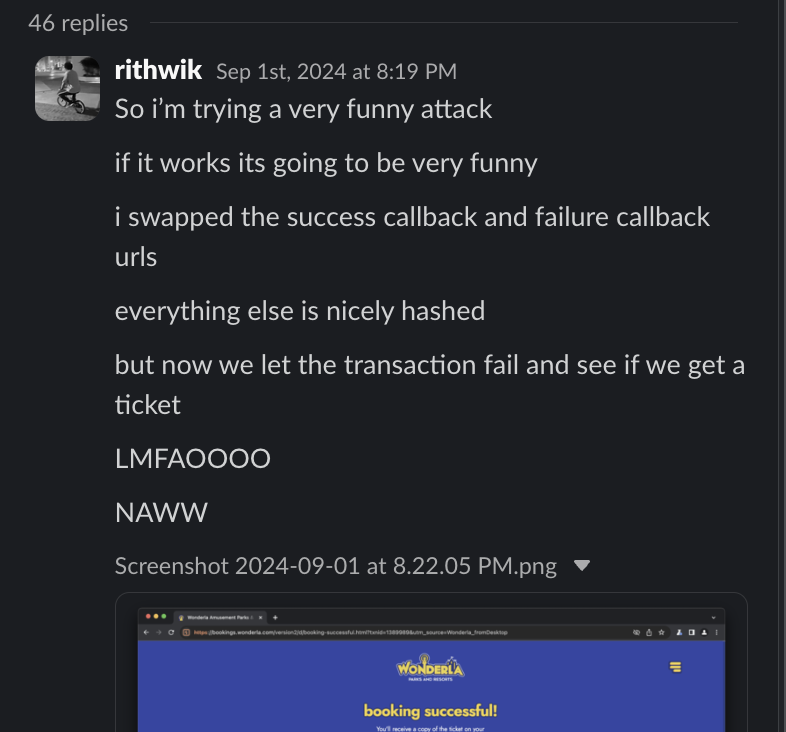
There's no way that this would work, right?
7
In essence, we're mapping:
Successful payment → failure_callback_url
Failed payment → success_callback_url
Of course, the merchant is supposed to later verify the transaction state with PayU directly, but I bet many won't bother. Including the amusement park.
Successful payment → failure_callback_url
Failed payment → success_callback_url
Of course, the merchant is supposed to later verify the transaction state with PayU directly, but I bet many won't bother. Including the amusement park.
8
I wasn't initially sure what had just happened: you don't expect this kind of dumb shit to work and it's a always a shock when it does.
Was super sick that day but I looked up PayU's reporting policy and realized that they had a Bugcrowd so I sent in a quickly recorded demo:
Was super sick that day but I looked up PayU's reporting policy and realized that they had a Bugcrowd so I sent in a quickly recorded demo:
2:07
9
And thus began the tiring process of disclosing this to PayU. Notes:
- My triagers on @Bugcrowd were awful, and never understood what I was trying to convey
- PayU India has abandoned their VDP, and all reports go to /dev/null.
- They also decided to test with my CC details???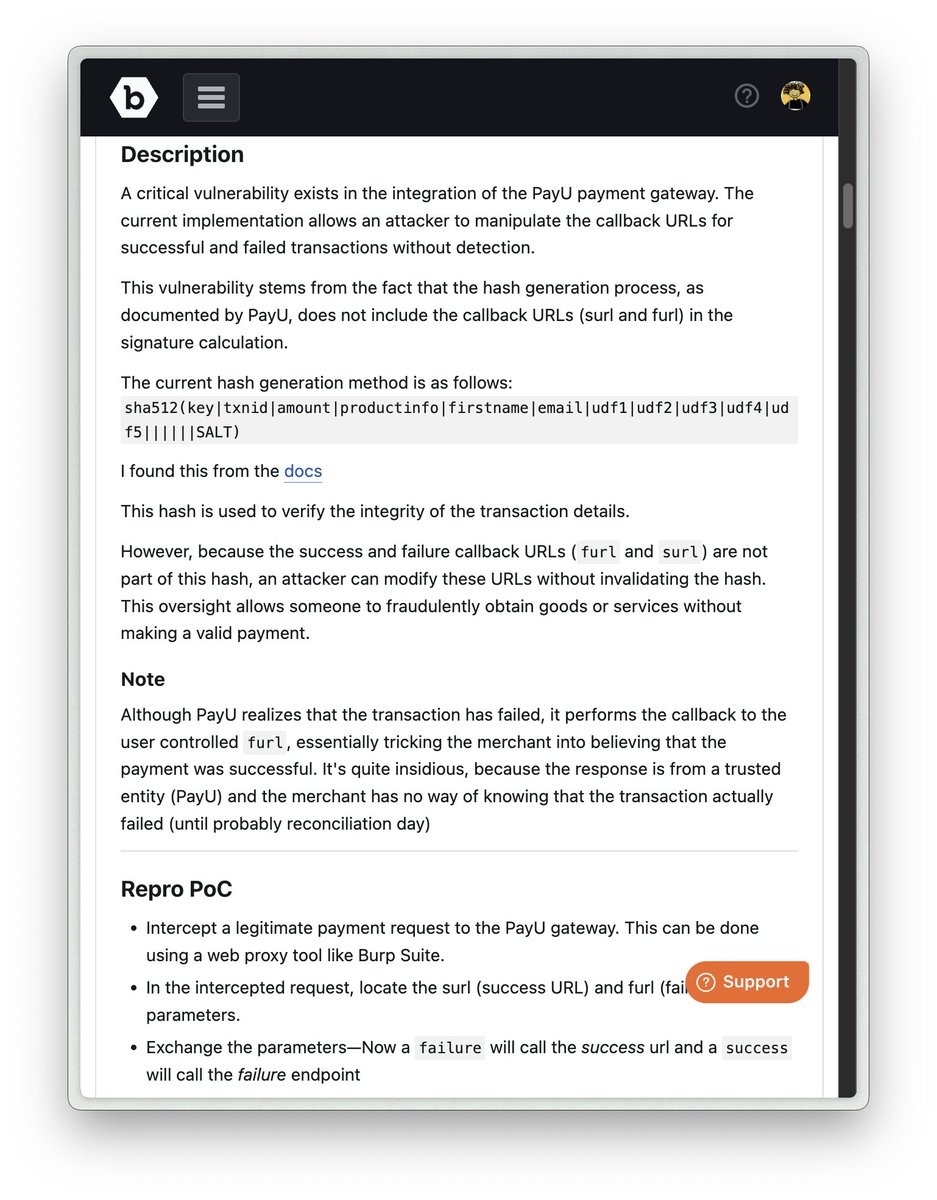
- My triagers on @Bugcrowd were awful, and never understood what I was trying to convey
- PayU India has abandoned their VDP, and all reports go to /dev/null.
- They also decided to test with my CC details???
10
It starts with the triager not understanding the vulnerability. I think they were hoping for some neat categorization, and this didn't obviously fit?
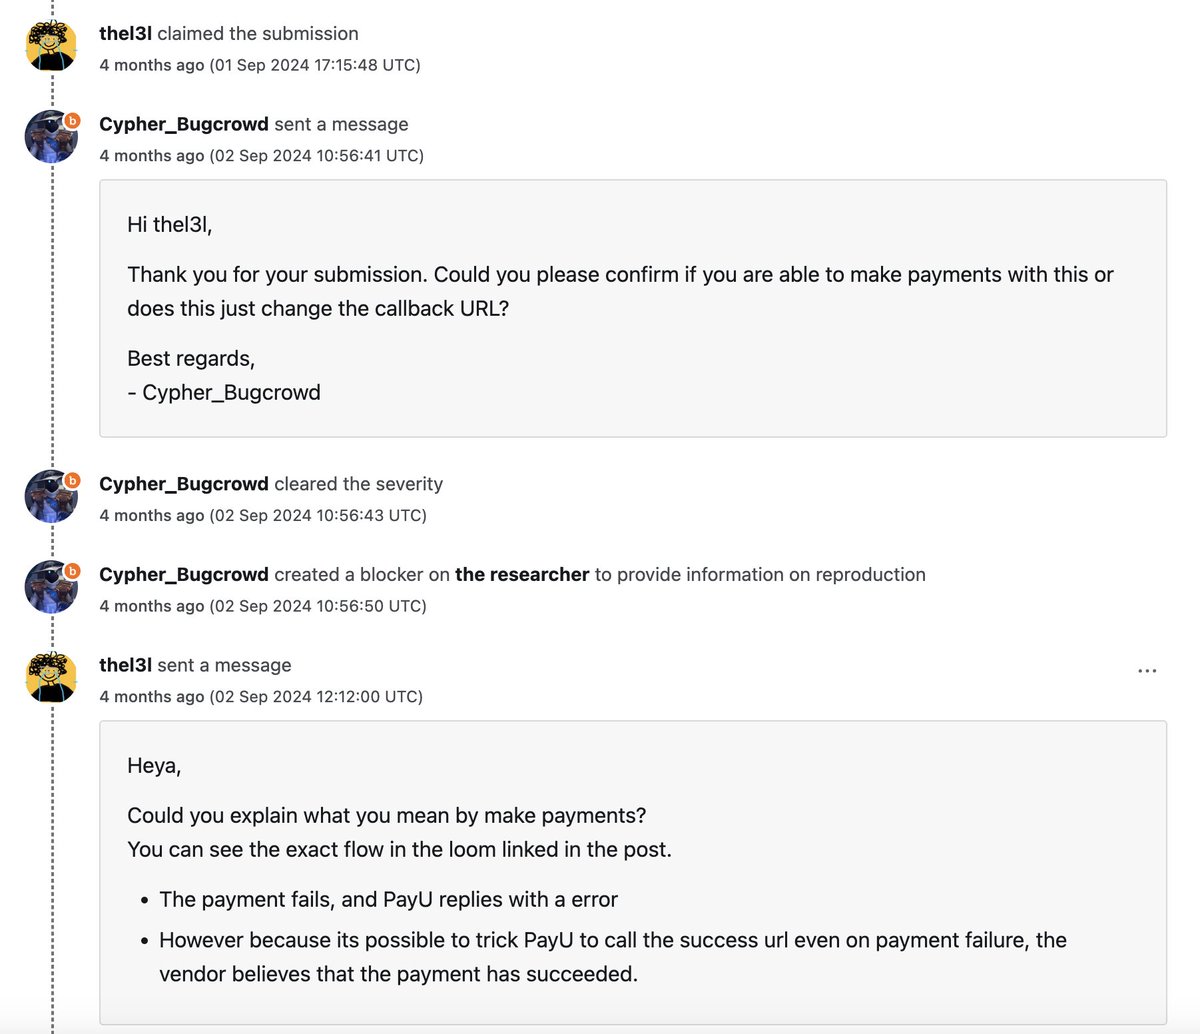
11
A week passes, I bump for update, and it's evident that I'm still talking to the wrong people

12
I'm tired by now, and have been trying to directly contact PayU as well. I had Claude write me a story to illustrate (this may have been a bit mean spirited, sorry lol)

13
Third triager decides that this is a waste of their time and tries to close the report:
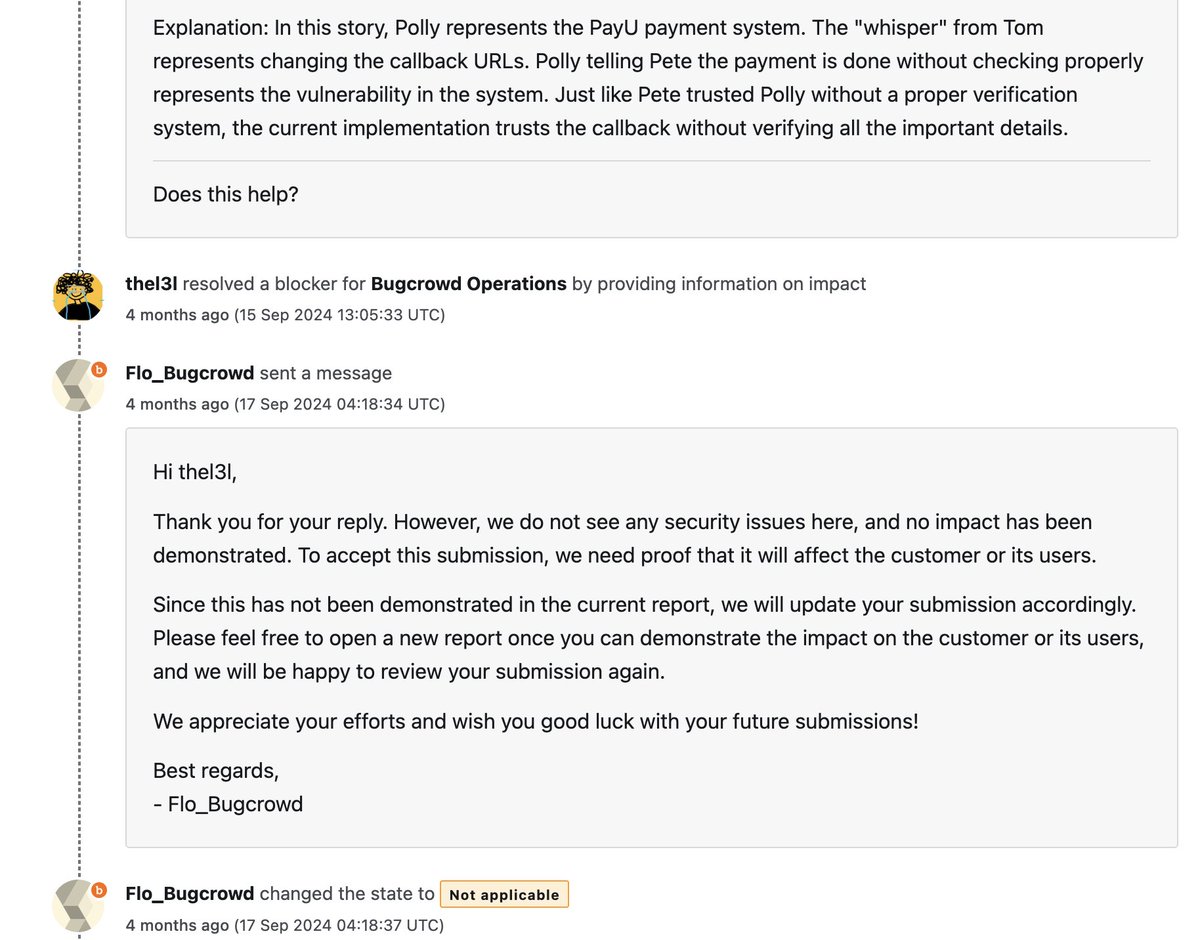
14
I request to be connected with someone at PayU directly, but to no avail.

15
Fourth triager joins the chat, and also insists I'm jerking them around.
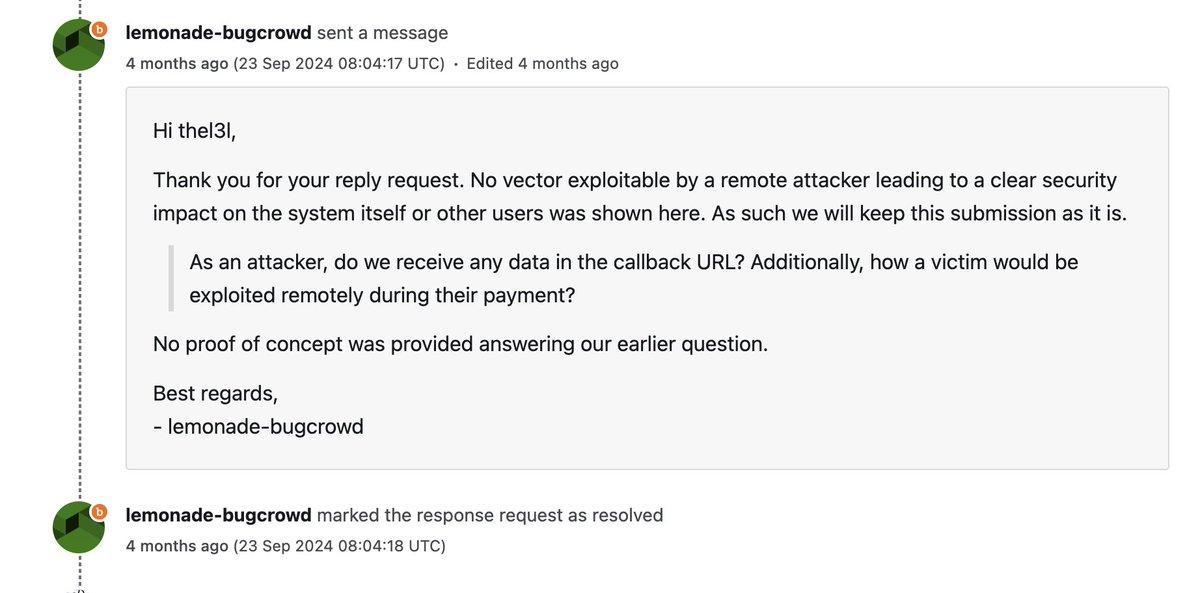
16
By now, I'd realized this was not going to work, so I shot off an email off to @IndianCERT with the details which turned out to be an *excellent* decision.
They were super professional and promptly acknowledged and set someone to interface with PayU directly after repro'ing!
They were super professional and promptly acknowledged and set someone to interface with PayU directly after repro'ing!
17
Everything goes silent for a while.
I've told CERT-In that I intend to disclose in 3 months which seems like a nice fair timeline.
Then one random evening, on October 4th, my credit card starts getting OTPs:
I've told CERT-In that I intend to disclose in 3 months which seems like a nice fair timeline.
Then one random evening, on October 4th, my credit card starts getting OTPs:
18
It took me a second to realize that I hadn't masked the CC number in my demo when I recorded the PoC in my sick/sleep deprived state.
Looks like it was my mistake to assume that no reasonable individual would use the *researcher's card* to test their system?
Looks like it was my mistake to assume that no reasonable individual would use the *researcher's card* to test their system?
19
I blocked my CC, and DM'ed CERT-In asking them to tell the PayU devs to knock it off—again, super nice of them.
I'd likely have gone ballistic if I had a direct line to PayU, because ???

I'd likely have gone ballistic if I had a direct line to PayU, because ???
20
Finally, CERT-In confirms that PayU has fixed the vuln on October 18th:

21
I never bothered to go back and look at how they 'fixed' their implementation, that's left as an exercise to the reader, but I forwarded the CERT thread to bugcrowd out of spite
They've not replied to a request for info in 4+ months, so I can only assume this is unmonitored.

They've not replied to a request for info in 4+ months, so I can only assume this is unmonitored.
22
In conclusion, disappointed with @PayUindia, would have been nice to have the VDP bounty paid out and the program either monitored or closed down.
Going to let CERT handle vendor comms for any disclosure going forward. I've sent in at least four reports since.
Cheers!
Going to let CERT handle vendor comms for any disclosure going forward. I've sent in at least four reports since.
Cheers!
